How do you deploy AI agents safely in production?
Implement changes in phases starting with read-only access, validate in discovery mode without write access, then carefully advance to execution under strict governance and oversight.
In phases, with read-only first. The pattern that works is: prepare the environment with scoped identity and audit, validate the agent in discovery mode where it can plan but not write, promote it to governed execution with tight tool boundaries and rollback, then run it under continuous governance with a standing review cadence. The single most common failure mode is granting write access before discovery-mode validation is honestly complete.
Reading
Related posts
 AI & Emerging Tech
Vibe coding is the easy part. The hard parts come later.
 AI & Emerging Tech
Probabilistic vs deterministic AI: a model guesses, so build what decides
 AI & Emerging Tech
Google Universal Cart: What It Means for eCommerce
 AI & Emerging Tech
Core dna MCP 2.0: build your own features, just by describing them
 AI & Emerging Tech
Recommendation engines: how recommender systems work and what’s changing for eCommerce
 AI & Emerging Tech
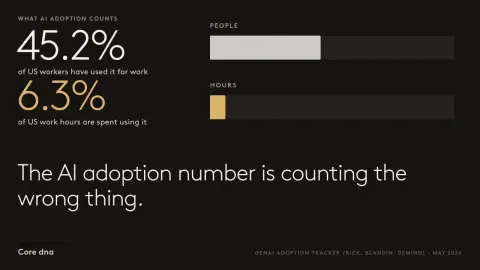
AI adoption rates count heads instead of work